IT, Cloud & Cybersecurity • Certification
Certified Information Security Manager
The management credential for security leaders.
Researched and maintained by TestPrepPilot Editorial BoardCloud, IT & cybersecurity certifications desk · Figures last verified August 2026
The short version
What is the Certified Information Security Manager and is it worth it?
CISM is a 150-question, 4-hour exam scored 450/800, costing $575 for members and $760 for non-members. Five years of security management experience (three in management) is required. It is valid three years with 120 CPE credits. Verify domain weights if testing after November 3, 2026.
- Recognised management-layer security credential
- Four domains weighted toward running the program
- Often required or preferred for CISO roles
- Pairs with CISA for audit-plus-management coverage
What is it?
What exactly is the Certified Information Security Manager?
The management credential for security leaders.
The Certified Information Security Manager (CISM) is ISACA’s credential for professionals who manage, design and govern an enterprise security program. It tests judgment from a manager’s perspective — governance, risk, program development and incident management — rather than hands-on tooling. Note a job-practice update takes effect November 3, 2026.
The path in brief
- Join ISACA
- Study the 4 domains
- Schedule via PSI
- Pass at 450/800
- Maintain 120 CPE/3yr
Before you book
Who is eligible to sit the Certified Information Security Manager?
Who it is for: Security managers, program leads and aspiring CISOs.
The test itself
What is the format of the Certified Information Security Manager?
The Certified Information Security Manager is administered by PSI test centre or remote proctoring and runs 4 hours, contains 150 multiple choice questions and requires 450 / 800 scaled to pass.
| Administered by | PSI test centre or remote proctoring |
|---|---|
| Questions | 150 multiple choice |
| Time limit | 4 hours |
| Pass mark | 450 / 800 scaled |
| Exam fee | $575 member / $760 non-member |
| Format | Multiple choice (scenario-based) |
Content outline
What topics are on the Certified Information Security Manager?
The Certified Information Security Manager is weighted across 4 domains; the largest are Information Security Program Development and Management (33%), Information Security Incident Management (30%), Information Security Risk Management (20%).
Weightings come from the official exam outline. Study time is best allocated in roughly these proportions rather than evenly across domains.
- Information Security Governance 17%
Strategy and alignment
- Information Security Risk Management 20%
Risk treatment
- Information Security Program Development and Management 33%
Building and running the program
- Information Security Incident Management 30%
Detection and response
Money & time
How much does the Certified Information Security Manager cost?
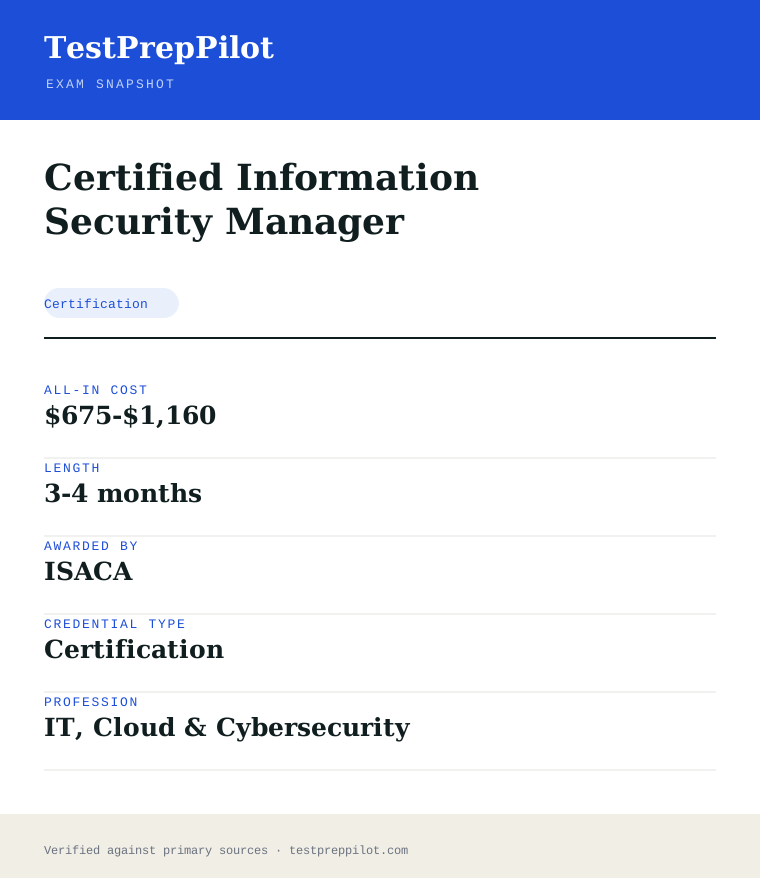
For the Certified Information Security Manager, the exam fee is $575 member / $760 non-member; the all-in cost is typically $675-$1,160; most candidates spend 3-4 months preparing.
Cost breakdown
| Exam fee | $575-$760 |
|---|---|
| Review manual/QAE | $100-$400 |
| Typical total | $675-$1,160 |
Domain weights change for exams from November 3, 2026; confirm current outline before studying.
Timeline
- Study 3-4 months
Typical prep: 3-4 months
The path
How do you register for the Certified Information Security Manager?
- 1
Register with ISACA10 minutes
Create an account; membership lowers the exam fee and unlocks study discounts.
- 2
Pay the exam fee
Members pay $575, non-members $760. A $50 application fee may apply for some credentials.
- Members: $575
- Non-members: $760
- 3
Schedule via PSI
Book a slot at a PSI test centre or choose remote proctoring.
- Test centre
- Remote proctored
- 4
Take the exam
Complete the 150-question exam and receive a scaled score.
The fine print
What are the retake and renewal rules for the Certified Information Security Manager?
- Proctoring & delivery
- ISACA exams are delivered by PSI at authorised test centres or through PSI remote proctoring, with a live proctor and secure-room requirements.
- Retake policy
- Candidates may attempt an exam up to four times in a rolling 12-month period: a 30-day wait before attempt 2, then 90-day waits before attempts 3 and 4. Each attempt requires a new registration fee.
- Score reporting
- Exams are scored on a 200–800 scale; 450 is the passing mark. Candidates see a preliminary pass/fail at the centre, with the official score following.
- Recertification
- Certifications are valid for three years. Holders must earn 120 CPE credits over the cycle (minimum 20 per year) and pay the annual maintenance fee ($45 members / $85 non-members).
What it pays
How much does this credential pay?
$182,510 median for computer and information systems managers (BLS, May 2024)
There is no Bureau of Labor Statistics occupation called "CISM" — the Certified Information Security Manager credential validates information-security management and governance skill, and the wage question belongs to the role you perform with it. The closest official BLS occupation is Computer and Information Systems Managers, SOC 11-3021, which had a May 2024 median wage of $182,510, with the lowest 10 percent under $105,680 and the highest 10 percent above $276,480, with Information Security Analysts (SOC 15-1212, $124,910) as the technical-side benchmark. The fit is deliberate: CISM holders work as security managers, security directors and information-security leadership, and the credential is positioned for the management tier — so the management series is the primary benchmark. BLS counted 610,800 computer and information systems manager jobs in 2024 and projects a 15 percent increase from 2024 to 2034, much faster than the average for all occupations, with about 38,900 openings a year. The limitation to state plainly: the BLS median covers the whole management occupation at all levels, credentialed or not, and the CISM's value is as a recognised security-management signal that employers use for leadership roles. Read the number as the market for the management roles the credential serves.
| Measure | Figure | Source / note |
|---|---|---|
| Median annual wage, computer and information systems managers | $182,510 | BLS OOH, SOC 11-3021, May 2024 |
| Lowest 10 percent | Under $105,680 | BLS OOH, SOC 11-3021, May 2024 |
| Highest 10 percent | Above $276,480 | BLS OOH, SOC 11-3021, May 2024 |
| Median, information security analysts (technical-side benchmark) | $124,910 | BLS OOH, SOC 15-1212, May 2024 |
Job growth.BLS projects a 15 percent increase for computer and information systems managers from 2024 to 2034, about 38,900 openings per year.
Source: BLS Occupational Outlook Handbook - Computer and Information Systems Managers
Your odds
What are the pass rates?
ISACA publishes pass rates — the reported CISM pass rate is around 50% in recent published data
ISACA publishes pass-rate information for its certification exams, and the reported CISM pass rate has historically clustered around 50 percent in recent published cycles; we present it as the body's own reporting, noting the figure varies by exam window and candidate pool. What ISACA also publishes is the format: the CISM exam has 150 multiple-choice questions with a 4-hour time limit, delivered by computer at ISACA-approved test centres or through remote proctoring, and the result is reported as pass/fail. The exam content follows the published CISM job practice areas: information security governance; information risk management and compliance; the information security program development and management; and the information security incident management. The practical reading: the published pass rate reflects a demanding management-level exam, and the strongest predictor of success is structured preparation — candidates who complete the review course, work the question database and meet the experience requirement (5 years of security work, including 3 years of management, with waivers) pass at higher rates than the overall cohort.
Read this before quoting the number.ISACA publishes pass-rate data that varies by window; the figure above is the recent reported range, not a fixed number.
Source: ISACA - Certified Information Security Manager (CISM)
Your schedule
How long should I study for it?
150-250 hours over 3-6 months (plus the 5-year experience requirement) of focused study
The CISM exam is a 150-question, 4-hour exam built on the four job practice areas: information security governance, information risk management and compliance, the security program development and management, and incident management. A defensible plan runs 150 to 250 hours over 3 to 6 months, built around the ISACA review materials and the 5-year management-experience requirement. Months 1-2: the governance and risk domains — the governance frameworks, the strategy and the alignment with business, then the risk-management process, the risk treatment and the compliance. Months 3-4: the program and incident domains — the security program development, the operations and the metrics, then the incident management lifecycle. Month 5: the question database and the full timed practice exams at the real 150-question, 4-hour format. The plan is management-framed because the CISM tests the leadership view of security, not the technical depth; candidates who study like engineers fail the governance and risk items.
- Months 1-270
Governance and risk
- Security governance and strategy
- The risk management process and compliance
- Business alignment and the frameworks
- Months 3-470
Program and incident
- Security program development and management
- Program operations and metrics
- Incident management lifecycle
- Month 545
Database and mocks
- The ISACA question database
- Two full timed practice exams
- Review weak domains
Adjusting the pace
Security manager in practice.The management view is familiar from the role; focus study on the exam format and the risk material.
Technical analyst adding management.Add 2-4 weeks of governance and risk-management fundamentals before the full plan.
How to study
How do I prepare most effectively?
The CISM rewards the management view of security, so the dominant strategy is studying the four job practice areas with a governance lens: the exam tests how security is governed, how risk is managed, how the program is built and run, and how incidents are managed — not the technical depth. Second, master the governance domain first — the frameworks, the strategy and the business alignment — because it anchors the credential's identity. Third, use the ISACA QAE (Questions and Answers Database) as the primary practice resource; it is the closest thing to the real item style and includes the rationales that build the reasoning. Fourth, confirm the experience requirement early: the CISM requires 5 years of security work including 3 years of management (with waivers), and certification cannot proceed without it. Finally, take at least two full timed practice exams at the real 150-question, 4-hour format; the length and stamina are part of the test.
Study the management view
Governance, risk, program and incident — not technical depth.
Master the governance domain
Frameworks, strategy and business alignment anchor the credential.
Use the ISACA QAE
The closest item style, with the rationales that build the reasoning.
Confirm the experience requirement
5 years of security work incl. 3 of management (with waivers).
Run two full timed mocks
150 questions in 4 hours; the stamina is part of the test.
What to buy
Which study resources are worth paying for?
CISM prep is dominated by ISACA's official materials. The ISACA CISM Review Manual ($100-$150) and the QAE database (about $200-$250, or included in the review course) are the standard stack; the review course runs roughly $500-$2,500 depending on format. Third-party books ($40-$100) and question banks ($50-$200) add alternatives. Free resources include the job practice areas outline and ISACA's sample questions. A realistic total budget is $600 to $3,000 including the exam fee (about $575 for ISACA members, $760 for non-members). Prices below are list prices as of mid-2026 and change frequently; we rank nothing by commission.
| Resource | Price | Format | Best for |
|---|---|---|---|
| CISM Review Manual | $100-$150 | Printed or digital book | The authoritative domain coverage |
| ISACA QAE database | $200-$250 | Online question database | The closest item style and rationales |
| ISACA review course | $500-$2,500 | Self-paced, virtual or in-person | Structured preparation |
| Third-party books and banks | $40-$200 | Books and practice items | Alternatives and extra volume |
| CISM exam | ~$575 member / ~$760 non-member | Computer-based exam | The certification itself |
List prices as of mid-2026, subject to change; ISACA fees vary by membership; no commission or affiliate ranking is implied.
Avoid these
What mistakes do candidates most often make?
The most common CISM mistake is studying like an engineer: candidates with a technical security background focus on the technical depth and fail the governance, risk and program items, which are the majority of the exam. The fix is a management-lens study plan. The second mistake is treating the four job practice areas as separate lists instead of a connected system — the exam tests how governance, risk, program and incident management work together. Third, candidates under-prepare the risk-management and compliance material, a distinct domain. Fourth, some candidates ignore the management-experience requirement until after passing and then wait years for certification; confirm it early. Finally, candidates who never run a full timed exam underestimate the 150-question, 4-hour stamina.
✕Studying like an engineer
✓The exam tests the management view; study governance and risk.
✕Treating the domains as lists
✓Learn how governance, risk, program and incident connect.
✕Under-preparing risk and compliance
✓A distinct domain; cover the risk process and compliance.
✕Ignoring the experience requirement
✓Confirm the 5-year requirement incl. 3 of management early.
✕Skipping full timed mocks
✓150 questions in 4 hours; run two full timed practice exams.
What you'll face
What question types will I see?
The CISM exam is a 150-question multiple-choice exam in 4 hours. The items span the four job practice areas with a management and governance concentration — many items present a security-management situation and ask for the correct leadership decision, framework application or program action. Samples below are editor-written illustrations of the published job practice areas, not live exam items; they show the management-decision style of the real items.
Strategy, frameworks, alignment and the security governance.
The risk process, treatment and compliance.
Program development, metrics and incident management.
Try these
Q1A new security program must be aligned with the business strategy. The most appropriate first step for the security manager is to:
Answer:A
Governance starts with business alignment — understanding the objectives and translating them into the security strategy. Tool deployment, hiring or skipping alignment each bypass the governance first step.
Q2After identifying a risk, the security manager should next:
Answer:A
The risk-management process analyses and evaluates the risk, then selects a treatment (accept, mitigate, transfer or avoid) aligned with the risk appetite — the structured step. Uniform acceptance, transfer or ignoring each fail the process.
Q3An incident response plan is most effective when it:
Answer:A
Effective incident management tests the plan regularly and integrates it with business continuity and communications — the management-level practice. Static, undocumented or disconnected plans each fail the incident-management domain.
Samples are editor-written illustrations of the published job practice areas, not live exam items.
The big day
What should I expect on exam day?
The CISM exam is a 150-question, 4-hour computer-based exam at an ISACA-approved test centre or through remote proctoring. Bring the required identification matching your registration and your exam confirmation; personal items go in the locker. Arrive early — late arrivals may forfeit the appointment and fee. Pace at about 1.6 minutes per item, flag uncertain items for review, and budget time for the reading-heavy scenario items. Your result is reported as pass/fail after the exam, with the official report following. If you do not pass, the retake policy and fee apply. On a pass, the CISM is valid for three years and is renewed by earning 120 continuing professional education (CPE) hours every three years. The afterwards matters: log your CPEs as you earn them, because ISACA audits renewals, and submit the certification application if you have not already completed it.
Bring
- Required identification matching your registration
- Exam confirmation
Leave at home
- Phone, smartwatch and all electronics
- Notes and study materials
- Personal bags beyond what the centre allows
How the day runs
Rules in the room
- The exam is computer-based and timed
- 4 hours for 150 questions; the clock does not pause
- The certification renews every 3 years with 120 CPEs
Afterwards.On a pass, complete the certification application and log 120 CPEs every three years. On a fail, retake per the ISACA policy after additional domain study.
Reference
What are the key facts about the Certified Information Security Manager?
Certified Information Security Manager is a certification credential; awarded by ISACA; the exam fee is $575 member / $760 non-member; typical preparation is 3-4 months; holders typically earn $120,000-$165,000.
| Credential | Certified Information Security Manager |
|---|---|
| Abbreviation | CISM |
| Type | Certification |
| Profession | IT, Cloud & Cybersecurity |
| Specialty | Cybersecurity (Vendor-Neutral) |
| Awarded by | ISACA |
| Difficulty | Hard |
| Typical prep time | 3-4 months |
| All-in cost | $675-$1,160 |
| Typical salary range | $120,000-$165,000 |
| Delivery | PSI test centre or remote proctoring |
| Retake | Up to 4 attempts/12mo; 30 then 90-day waits |
| Validity | 3 years; 120 CPE + $45/$85 annual fee |
| Scope | National / Multi-state |
| Also known as | CISM |
Real questions
Frequently asked questions about the Certified Information Security Manager
Is CISM harder than CISSP?
They differ in kind: CISM tests management judgment (govern, risk, program, incident), while CISSP is broader technical-and-management depth. Many technical people fail CISM by answering as engineers rather than managers.
What is the pass mark?
A scaled 450 out of 800; the exam is scenario-based and weighted toward program management.
Are the domain weights changing?
Yes. ISACA has a CISM update effective November 3, 2026; verify the current weightings if you test after that date.
How do I renew CISM?
Earn 120 CPE credits over three years and pay the annual maintenance fee ($45 members / $85 non-members).
Why is the ISACA passing score 450?
ISACA uses a scaled 200–800 range; 450 is the fixed threshold, not a raw percentage. Scenario-based items are weighted by difficulty.
Can I sit the exam without the experience?
Yes for most credentials. You can pass first and have five years afterward to submit verified experience.
In short
Is the Certified Information Security Manager worth it?
- CISM is ISACA’s security management cert
- 150 questions, 4 hours, 450/800, $575-$760
- Four domains; 5yr exp (3yr management)
- 3-year validity; 120 CPE. Weights update Nov 2026
Same awarding body
What other credentials does ISACA award?
Worth comparing
How does the Certified Information Security Manager compare with similar credentials?
Trust
Where does this information come from?
Everything above is taken from the awarding body's own published material. Fees, question counts and domain weights are revised regularly — check the official page before you pay.
- ISACA Awarding body
- Official Certified Information Security Manager exam page Exam page
- ISACA certification programme Programme rules
Research confidence: high · Last reviewed 2026-08