The short version
What is the CompTIA Cybersecurity Analyst (CySA+) and is it worth it?
CySA+ (CS0-003) is a single exam proving you can use threat and vulnerability data to detect, analyze and respond to security incidents.
- Defensive focus
- Maps to DoD 8140
- Good step after Security+
What is it?
What exactly is the CompTIA Cybersecurity Analyst (CySA+)?
Move from defense to threat analysis
CompTIA Cybersecurity Analyst (CySA+) certifies the behavioral analytics and incident-response skills used in defensive security operations, including vulnerability management and threat hunting.
Before you book
Who is eligible to sit the CompTIA Cybersecurity Analyst (CySA+)?
Who it is for: SOC analysts and threat hunters
The test itself
What is the format of the CompTIA Cybersecurity Analyst (CySA+)?
The CompTIA Cybersecurity Analyst (CySA+) is administered by Pearson VUE and runs 165 minutes, contains 85 questions and requires 750 of 900 to pass.
| Administered by | Pearson VUE |
|---|---|
| Questions | 85 |
| Time limit | 165 minutes |
| Pass mark | 750 of 900 |
| Exam fee | $404 |
| Format | Multiple-choice and performance-based |
Content outline
What topics are on the CompTIA Cybersecurity Analyst (CySA+)?
The CompTIA Cybersecurity Analyst (CySA+) is weighted across 4 domains; the largest are Security operations (33%), Vulnerability management (30%), Incident response and threat hunting (20%).
Weightings come from the official exam outline. Study time is best allocated in roughly these proportions rather than evenly across domains.
- Security operations 33%
- Vulnerability management 30%
- Incident response and threat hunting 20%
- Compliance and reporting 17%
Money & time
How much does the CompTIA Cybersecurity Analyst (CySA+) cost?
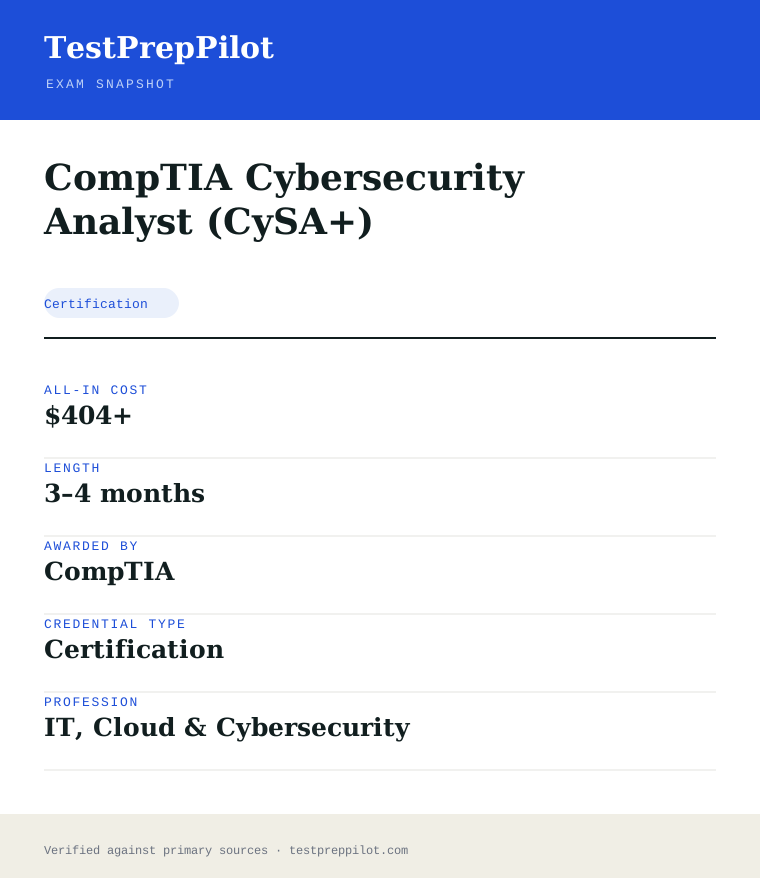
For the CompTIA Cybersecurity Analyst (CySA+), the exam fee is $404; the all-in cost is typically $404+; most candidates spend 3–4 months preparing.
Cost breakdown
| Exam voucher | $404 |
|---|---|
| Typical total | $404+ |
Academic pricing available.
Timeline
- Study + labs 8–12 weeks
- Sit CS0-003 test day
Typical prep: 3–4 months
The path
How do you register for the CompTIA Cybersecurity Analyst (CySA+)?
- 1
Create your accounts10 minutes
Set up a free CompTIA account and a Pearson VUE account. Your CompTIA account is where the certification and CEUs are tracked; Pearson VUE handles scheduling and delivery.
Use a consistent email so your exam result links to your CompTIA record.
- 2
Purchase an exam voucher1 day
Buy the XK0-006 voucher from the CompTIA store (standard $390 USD). Optionally choose an exam+retake bundle or add CertMaster training.
- Select Linux+ (XK0-006) in the CompTIA store
- Choose voucher only, exam+retake bundle, or bundle with training
- Save the voucher code from your CompTIA account
- 3
Schedule your exam15 minutes
Go to Pearson VUE, enter your voucher code, and book a date. Choose a nearby test center or online proctoring (OnVUE).
- Pick test center or OnVUE online
- Run the OnVUE system check if testing at home
- Confirm date, time, and time zone
- 4
Prepare your ID and environmentTest-day prep
Bring a government-issued photo ID to a center. For online testing, prepare a quiet private room, clear your desk, and have your webcam ready for the check-in scan.
Accepted ID rules follow Pearson VUE policy (typically passport or driver's license matching your account name).
- 5
Take the exam90 minutes
Complete up to 90 questions in 90 minutes, including multiple-choice and performance-based items. You see a pass/fail result on screen immediately after finishing.
- 6
Claim and maintain your certificationA few days
Your certification appears in CompTIA CertCentral. Log in to download the e-certificate and start tracking the 50 CEUs needed to renew within 3 years.
The fine print
What are the retake and renewal rules for the CompTIA Cybersecurity Analyst (CySA+)?
- Proctoring & delivery
- Delivered by Pearson VUE with two options: an in-person proctored test center, or online proctoring via OnVUE with a live remote proctor (requires webcam, stable internet, and a private room).
- Retake policy
- If you do not pass, you may retake XK0-006 after a 14-day waiting period. Each attempt requires a new exam voucher; there is no limit on the number of retakes. CompTIA's standard candidate agreement governs retake rules.
- Score reporting
- A pass/fail result is shown on screen immediately after the exam. A detailed score report by domain is available in your Pearson VUE account and mirrored in your CompTIA CertCentral record.
- Recertification
- Linux+ is valid for 3 years from the certification date. Renew by earning 50 Continuing Education (CE) credits and paying the CE fee through CompTIA CertCentral, by earning a higher-level CompTIA certification, or by passing the current XK0-006 exam again.
- Refunds & rescheduling
- Exam vouchers are generally non-refundable but may be transferable or have a defined expiry; optional CertMaster training may be refundable within a limited window per CompTIA's terms. Review voucher terms at purchase.
Context
Linux certifications compared
| Credential | Vendor | Level | Exam | Validity | |
|---|---|---|---|---|---|
| CompTIA Linux+ | CompTIA | Vendor-neutral | Intermediate | 1 exam (XK0-006) | 3 years |
| LPIC-1 | Linux Professional Institute | Vendor-neutral | Entry | 2 exams (101 + 102) | 5 years |
| Red Hat RHCSA | Red Hat | Vendor-specific | Entry | 1 exam (performance lab) | 3 years |
What it pays
How much does this credential pay?
$124,910 median for information security analysts (BLS, May 2024)
There is no Bureau of Labor Statistics occupation called "Cybersecurity Analyst" exactly, but Information Security Analysts (SOC 15-1212) is the official category that maps most directly to the CySA+ role, and we have chosen it deliberately because CompTIA positions CySA+ as the mid-level, analyst-side certification — the one you sit after the entry-level Security+ and before the expert-level CASP+. A CySA+ holder works in a security operations centre or on a defensive security team: monitoring, detecting, analysing and responding to threats, which is precisely the day-to-day described under the information security analyst occupation. That occupation had a May 2024 median wage of $124,910, with the lowest 10 percent earning under $69,660 and the highest 10 percent earning more than $186,420. The distribution is worth reading carefully because the CySA+ is the credential that typically moves someone from a general IT or junior SOC role into the higher band of this occupation — the 29 percent projected growth is the strongest of any occupation covered on this site, and it reflects sustained demand for defensive analysts rather than for any single certificate. BLS projects 29 percent employment growth for information security analysts from 2024 to 2034, far faster than the average for all occupations, with roughly 16,000 openings a year arising from both growth and replacement. The most important caveat for a CySA+ candidate is that the certificate is a validation of analyst capability, not a job title in itself — the wage figure above measures the whole information-security-analyst occupation, not CySA+ holders narrowly, and should be read as the destination role’s compensation rather than a guaranteed CySA+ outcome. It is also the role most exposed to the AI-in-security shift that V4 now tests explicitly.
| Measure | Figure | Source / note |
|---|---|---|
| Median annual wage, information security analysts | $124,910 | BLS Occupational Outlook Handbook, May 2024 |
| Lowest 10 percent | less than $69,660 | BLS OOH Pay tab, May 2024 |
| Highest 10 percent | more than $186,420 | BLS OOH Pay tab, May 2024 |
| Employment, 2024 | 182,800 jobs | BLS OOH Quick Facts, 2024 |
| Projected annual openings | ~16,000 per year | BLS OOH Job Outlook, 2024-34 |
Job growth.29% projected change 2024-34 (much faster than average), ~16,000 openings a year; CySA+ is the mid-level analyst credential for this occupation, and V4 now tests AI-in-security explicitly
Source: BLS Occupational Outlook Handbook — Information Security Analysts
Your odds
What are the pass rates?
CompTIA publishes no pass rate — but it does publish the passing score: 750 out of 900
CompTIA does not release pass-rate statistics for CySA+ or any of its certifications, and it never has. Unlike some vendors, however, it does publish the cut score, and understanding what that number means is more useful than any rumoured pass rate. CS0-004 is scored on a scale of 100 to 900 and you need 750. That is not a percentage of the questions. CompTIA equates every exam form so that a harder set of items demands the same underlying ability as an easier one, and performance-based questions carry more weight than a single multiple-choice item, so the raw-to-scaled conversion is not linear and cannot be reverse-engineered. Candidates who aim for "83 percent on practice tests" are using a heuristic that does not map onto the scoring model; aim instead to be able to complete every performance-based analysis task unaided. The retake policy matters more than a pass rate: CompTIA imposes no waiting period between your first and second attempt, so a narrow fail can be re-sat almost immediately, but from the third attempt onward you must wait 14 calendar days between sittings, and every attempt is paid at full price unless you bought a retake bundle or a voucher with a retry. The score report gives you the outcome and your scaled score on screen the moment you finish, plus a printed report showing relative performance by domain — that report is the closest thing to diagnostic feedback available, and it turns a failed attempt into an actionable study plan rather than guesswork. We have deliberately left the pass-rate table empty because no authoritative figure exists.
Read this before quoting the number.No pass rate is published by CompTIA, by Pearson VUE, or by the accreditation that CySA+ carries. We have deliberately left the pass-rate table empty. What is published and verifiable is the 750/900 cut score and the retake schedule, which is what the narrative above covers instead.
Your schedule
How long should I study for it?
100-130 hours of focused study
The first thing to establish is which exam you are actually studying for, and for CySA+ this is now the most important sentence on the page. CS0-004 — CySA+ version 4 — launched on 23 June 2026 and is the current exam. CS0-003 (version 3) remains available for English testing until 22 December 2026, after which English candidates must sit CS0-004; translated-language versions of CS0-003 retire on 23 March 2027. CS0-004 is not a light refresh: it added explicit coverage of artificial intelligence in security operations — AI used in defensive tooling, AI governance, and AI-specific risks such as model hallucination and data exposure — alongside the traditional analyst domains. If you buy a 2024 or earlier CySA+ book you are studying version 3 and will have real gaps. The current domain weights are Security Operations 34 percent, Vulnerability Management 26 percent, Incident Response and Management 24 percent, and Reporting and Communication 16 percent. Notice that Security Operations plus Vulnerability Management are 60 percent of the paper — together they are the core of the analyst job — while Reporting and Communication, though only 16 percent, is where version 4 candidates most often lose cheap points because it is easy to under-prepare the communication side. CompTIA recommends about four years of hands-on security or SOC-analyst experience before sitting, so the plan below assumes you have that baseline or its equivalent in lab work. A realistic window is ten to twelve weeks at 10-12 hours a week, and it must include log, packet and vulnerability-data analysis practice, because the performance-based questions hand you real-looking telemetry and ask you to interpret it.
- Week 110-12 hrs
Confirm version and build the analysis lab
- Confirm you are registered for CS0-004 (V4), not CS0-003 — check the exam code on your voucher
- Stand up a lab: a SIEM or log-source you can query, a packet capture tool, and a vulnerability scanner trial
- Read the official CS0-004 objectives end to end and map every task to a domain weight
- If you own V3 material, set it aside except where the domain content is unchanged
- Weeks 2-411-13 hrs/week
Domain 1 — Security Operations (34%)
- Process and analyse security telemetry: logs, alerts, network flow and endpoint data
- Tune and interpret detection logic; understand false positives and the analyst’s triage workflow
- Cover the V4 AI-in-security operations material: how defensive tooling uses AI and where it helps or misleads
- Practise reading a packet capture and a SIEM query result until interpreting them is routine
- Weeks 5-610-12 hrs/week
Domain 2 — Vulnerability Management (26%)
- Run a vulnerability scan in your lab and prioritise findings by exploitability and asset value
- Map findings to frameworks (e.g., CVE/CVSS) and to remediation, not just detection
- Understand assessment methodology: authenticated vs unauthenticated scans, scope and false negatives
- Practise writing a prioritised remediation recommendation from a raw scan export
- Weeks 7-811-13 hrs/week
Domain 3 — Incident Response and Management (24%)
- Learn the incident-response lifecycle: preparation, detection, analysis, containment, eradication, recovery, lessons learned
- Practise analysing an incident from indicators to a containment decision using provided data
- Cover the V4 AI risk material: model hallucination, data exposure and governance of AI use in security
- Drill the communication handoffs between detection, response and reporting stages
- Week 910-12 hrs
Domain 4 — Reporting and Communication (16%)
- Practise writing an incident report and a vulnerability summary for both technical and executive audiences
- Learn stakeholder communication, severity rating and the structure of a clear post-incident review
- Do not skip this domain — it is small but where V4 candidates lose avoidable points
- Rehearse explaining a technical finding to a non-technical reader in plain language
- Weeks 10-1210-12 hrs/week
Performance-based question rehearsal and timed exams
- Sit three full 165-minute practice exams weighted to the four current domains
- Rehearse performance-based items: interpret a log or capture and state the attack and the next step
- Re-lab every miss against the V4 objectives rather than re-reading it
- One quiet day before the exam; confirm your V4 registration and ID details
Adjusting the pace
Working SOC analyst with 4+ years.Six to eight weeks. The domain content is your day job; spend the recovered time on the V4 AI additions and on the Reporting/Communication domain, which practising analysts often under-prepare.
Security+ holder moving up.Twelve to fourteen weeks. You have the security fundamentals but lack analyst depth; invest the extra weeks in hands-on telemetry and vulnerability analysis, because CySA+ tests interpretation, not definitions.
Career-changer with a homelab, no SOC experience.Sixteen or more weeks. You must build the analyst intuition from scratch in a lab — packet captures, SIEM queries, scan outputs — because the performance-based questions assume you have interpreted real telemetry before.
How to study
How do I prepare most effectively?
CySA+ is the exam on this site that most rewards hands-on interpretation over memorisation. Where Security+ tests that you know a concept exists, CySA+ hands you a log, a packet capture or a vulnerability scan and asks you to read it and decide. The single most useful habit is therefore to train interpretation deliberately: every time you study a detection or a vulnerability, generate or obtain the actual data it produces and practise drawing the conclusion the exam expects. Candidates who read about SIEM rules but have never written a query, or who memorise CVSS formulas but have never prioritised a real scan, consistently lose the performance-based points that decide a 750/900 pass.
Study the current CS0-004 blueprint, not version 3
CS0-004 launched 23 June 2026 and adds explicit AI-in-security coverage — AI used in defensive operations, AI governance, and AI risks such as hallucination and data exposure. CS0-003 English retires 22 December 2026. Version 3 books and courses are still on sale and still rank in search; check the exam code on your voucher and any material you buy, and treat V3 resources as partially obsolete.
Interpret real telemetry, not descriptions of it
The performance-based questions give you logs, packet captures or scan output and ask what is happening and what to do next. Build a lab with a SIEM or log source, a packet tool and a scanner, and practise reading the actual artefacts. The candidate who has queried a SIEM and prioritised a real scan answers these items from experience; the one who only read about them freezes.
Weight study to Security Operations and Vulnerability Management
Those two domains are 34% and 26% — 60% of the paper together. They are also the most performance-based-heavy. Allocate accordingly and resist over-investing in the 16% Reporting domain at their expense, while still not skipping it, because it is where V4 candidates drop cheap points.
Learn the V4 AI-in-security material as a real domain, not a footnote
Version 4 made AI explicit: how defensive tooling uses AI, the governance of that use, and the new risks AI introduces — model hallucination producing false conclusions, and data exposure through AI-assisted analysis. These appear as both knowledge and scenario items. Treat them as examinable content equal to any other, not as a token update.
Do the performance-based questions last, and know that you can
CompTIA presents PBQs early but allows you to skip and return, which is the key tactical difference from a fixed-order exam. Mark every PBQ, clear the multiple-choice at a fast tempo, then divide remaining time across the outstanding tasks. Candidates who work in presented order spend the first hour on two PBQs and then rush the multiple choice.
Use the post-exam score report as a study instrument
CompTIA gives your scaled score and a domain-by-domain breakdown on screen and in a printed report. If you must retake, that breakdown is the most actionable diagnostic available anywhere on this site — identify the one or two domains that dragged the 750 down and drill those specifically rather than re-sitting on the same preparation.
What to buy
Which study resources are worth paying for?
The buying decision for CySA+ is, as with every CompTIA exam, first and foremost about version: CS0-004 material is new as of its June 2026 launch, and CS0-003 books and courses are still widely sold and ranked. Buy anything labelled CS0-004 or "V4", and verify the AI-in-security content is actually present rather than promised. The other decision is whether to pay for CompTIA’s own bundles, which add labs and a retake to the voucher at a premium. The exam voucher itself carries a list price around $439, and the certification is renewed over three years with 60 continuing-education units and a $150 CE fee.
| Resource | Price | Format | Best for |
|---|---|---|---|
| Exam voucher (CS0-004) | ~$439 CompTIA US list; resellers often lower | Pearson VUE, test centre or online | Required — buy the voucher alone if you already have a lab |
| CompTIA CertMaster bundles (Perform + Practice) | Bundle pricing at the CompTIA Store; includes voucher and often a retake | eLearning with labs plus adaptive practice | Candidates without their own SOC-style lab |
| Your own lab — SIEM/log source, packet tool, scanner trial | Free to low cost | Self-built | The most valuable resource for a performance-based-heavy exam |
| Jason Dion CySA+ course (Udemy) | ~$15-30 in Udemy sales | Video + practice exams | Structured video with a large practice-question bank — verify it is the V4 edition |
| CySA+ Study Guide (Sybex / Wiley) | ~$50-60 list | Print + eBook with test bank | Ordered reference — confirm the CS0-004 edition before buying |
| Official CompTIA CySA+ objectives and CertMaster Practice | Objectives free; Practice paid | PDF / web + online | The authoritative blueprint to study against |
Prices checked 2026-08 in USD before tax. CompTIA voucher list is ~$439 and varies by region and promotion; Udemy sale prices are far below list. Confirm any course is the CS0-004 (V4) edition, since CS0-003 material remains on sale. We do not rank by commission.
Avoid these
What mistakes do candidates most often make?
CySA+ mistakes divide into two groups: version errors that did not exist a year ago, and the perennial ones — studying an interpretation exam by reading, and mismanaging a 165-minute clock against performance-based items that take real time. The version trap is especially sharp here because CS0-004 is new and its AI content is genuinely new, so a candidate using a 2024 book is not merely slightly behind but missing an examinable domain.
✕Studying CS0-003 (V3) material for a CS0-004 (V4) exam
✓CS0-004 launched 23 June 2026 with explicit AI-in-security coverage; CS0-003 English retires 22 December 2026. V3 books and courses are still on sale and rank highly in search, and they omit the V4 AI material entirely. Check the exam code on your voucher and any resource you buy, and treat V3 material as partially obsolete rather than a syllabus.
✕Preparing by reading instead of interpreting telemetry
✓CySA+ performance-based questions hand you logs, packet captures and scan output and ask you to read them. A candidate who has read about SIEM rules but never queried one, or memorised CVSS but never prioritised a real scan, is not ready. Convert at least a third of study hours into interpreting actual artefacts in a lab.
✕Skipping or under-preparing the Reporting and Communication domain
✓At 16% it looks small, but it is where V4 candidates lose cheap, avoidable points because technical analysts neglect communication. Practise writing an incident report and a vulnerability summary for both technical and executive readers; the exam tests that you can explain a finding, not just find it.
✕Treating the V4 AI content as a token update
✓Version 4 made AI explicit and examinable: AI in defensive operations, AI governance, and AI risks — hallucination and data exposure. Candidates who read "AI" in a changelog and move on miss scenario items. Study it as a real content area equal to any other domain.
✕Spending the first hour on the performance-based questions
✓CompTIA presents PBQs early but allows skipping and return. Mark them all, clear the multiple-choice quickly, then allocate remaining time deliberately across the outstanding tasks. Candidates who work in presented order run out of clock on the items that decide the 750 pass.
✕Forgetting the certification expires and costs to renew
✓CySA+ is valid three years under CompTIA CE, renewed with 60 CEUs and a $150 CE fee over that period. Candidates often treat it as permanent. Diary the expiry on the day you pass and bank CEUs from real security work rather than scrambling in year three; a higher CompTIA certification can renew it automatically.
What you'll face
What question types will I see?
A maximum of 85 questions in 165 minutes (two hours and forty-five minutes), scored on a 100-900 scale with a 750 cut. The paper mixes multiple choice — single-answer and multiple-response — with performance-based questions that present a realistic analyst artefact: a log extract, a packet capture, a vulnerability scan, or an incident timeline, and ask you to interpret it and state the attack, the root cause, or the next response step. PBQs carry more weight than a single multiple-choice item, but you may skip them and return, so the presented order is not the order to work in. The four current domains are Security Operations (34%), Vulnerability Management (26%), Incident Response and Management (24%), and Reporting and Communication (16%). Because CompTIA equates forms, your scaled score is not a percentage of items correct and cannot be converted into one. Version 4 added explicit AI-in-security items — both knowledge questions about AI use in defensive operations and governance, and scenario items about AI-introduced risks such as hallucinated conclusions and data exposure. The practical pacing implication is that multiple-choice items should average well under a minute so the PBQs, which can consume several minutes each, have somewhere to come from within the 165-minute window.
A realistic artefact — log, capture, scan, timeline — with an interpretation or response task. Skippable and returnable, which is the key tactical difference from a fixed-order exam.
Detection logic, framework knowledge, tool purpose, policy. Distractors are usually plausible analyst actions that are subtly wrong in sequencing or scope.
The stem states how many to select and scoring is all-or-nothing. Common where several steps together complete an investigation or remediation.
Knowledge and scenario items on AI use in defensive operations, AI governance, and AI risks such as hallucination and data exposure. Genuinely new in CS0-004 and easy to miss if studying V3 material.
Try these
Q1An analyst reviews a SIEM alert showing a sudden spike in outbound DNS queries from a single workstation to many random subdomains of an unknown domain, with each response under 200 bytes. The workstation’s egress to the internet is otherwise normal. Which conclusion is most supported?
Answer:A
High-volume DNS queries to many random subdomains with small response sizes is a classic DNS-tunneling exfiltration pattern: an attacker encodes data in subdomain labels to smuggle it out past egress controls that permit DNS. B is wrong because a cache refresh does not target random unknown subdomains at volume. C is wrong because a DDoS would aim traffic at a victim, not generate random lookups from one host. D is wrong because TTL misconfiguration would not produce this query pattern. The V4 exam rewards reading the telemetry rather than recognising a buzzword.
Q2A vulnerability scanner reports a finding with CVSS base score 9.8 on an internet-facing web server, and a separate finding scored 7.5 on an internal print server. From a remediation-prioritisation standpoint, which action is correct?
Answer:B
Prioritisation weights exploitability and exposure alongside the CVSS score; a 9.8 on an internet-facing asset is both highly severe and directly exposed, so it leads. A is a common trap — ease of remediation is not a prioritisation criterion. C invents a requirement the analyst role does not impose; scanning findings drive remediation directly. D confuses throughput with risk. This is the Vulnerability Management domain (26%), where CySA+ tests judgement, not just score recall.
Q3A security team begins using an AI-assisted analysis tool that ingests case data, including customer PII, to draft incident summaries. Which risk introduced specifically by the AI use must the governance process address?
Answer:B
Two V4-specific risks are in play: the model can hallucinate — produce confident but false conclusions an analyst might accept — and sending customer PII to an externally hosted model can expose that data to the provider, a governance and compliance concern. A is false; models do not typically refuse PII outright. C is false; AI does not autonomously encrypt. D is dangerous practice, not a feature — human review remains required. This item reflects the explicit AI-in-security coverage new to CS0-004.
Samples are editor-written illustrations of the published CS0-004 blueprint, not live exam items.
The big day
What should I expect on exam day?
One hundred sixty-five minutes, up to 85 questions, delivered through Pearson VUE either at a test centre or online with OnVUE proctoring. Two things about a CompTIA exam day differ sharply from a fixed-order exam and both are in your favour. First, you can navigate: performance-based questions are presented early and you are permitted to skip them and return, and you can review and change multiple-choice answers before submitting. Build your pacing plan around that — mark every PBQ, sweep the multiple choice at a brisk tempo, then divide what remains across the outstanding tasks. Second, you get your result immediately: the scaled score appears on screen the moment you submit, plus a report showing relative performance by domain, which is genuinely diagnostic if you have to come back. For CySA+ specifically, the performance-based items hand you telemetry — logs, captures, scans — so the single biggest on-the-day risk is spending the first hour on two PBQs and rushing the multiple choice that decides the 750. The thing that goes wrong most often has nothing to do with security: CompTIA requires two forms of identification, one government-issued photo ID, and the name must match your CompTIA account exactly. Check your account spelling the week before; correcting it on the day is not possible and the seat is lost. Confirm you are booked for CS0-004, not CS0-003, before you travel.
Bring
- Two forms of identification, both unexpired, with names matching your CompTIA account exactly
- One must be a government-issued photo ID; the second must carry your name and signature (a credit card is usually accepted)
- Your CompTIA ID, in case check-in cannot locate the booking
- For OnVUE: a phone for check-in photographs, a completely clear desk, and a private room with a door you can close
- For OnVUE: a webcam, microphone and connection already system-tested on the exact machine you will use
Leave at home
- Phones, smartwatches, fitness trackers and earbuds — locker at a centre, out of the room for OnVUE
- All notes, cheat sheets and printed command or framework references
- Your own paper and pens; a test centre issues an erasable noteboard and OnVUE provides a digital whiteboard only
- Bags, coats, hats, food and drink beyond what the centre permits
- Second monitors, which must be unplugged and turned away for OnVUE, and any other person in the room
How the day runs
Rules in the room
- Navigation is permitted: you may skip performance-based questions and return, and review multiple-choice answers before submitting.
- Passing score is 750 on a 100-900 scale; it is not a percentage of items correct.
- Two forms of ID are required, one government-issued with photo, names matching your CompTIA account exactly.
- No scheduled breaks in a 165-minute exam, and the clock does not stop if you leave.
- Erasable noteboard only at a test centre; OnVUE candidates get a digital whiteboard and no physical writing materials.
- No waiting period between first and second attempt; from the third attempt onward you must wait 14 calendar days; each attempt is paid unless a retake was bundled.
- CS0-004 is the current exam (launched 23 June 2026); CS0-003 English retires 22 December 2026.
Afterwards.Your pass or fail and your scaled score appear on screen the instant you submit, and you leave a test centre with a printed score report showing how you performed relative to each of the four domains. That report is the most useful artefact any of these exams produces, so read it properly rather than filing it. On a pass, your certification appears in your CompTIA account within a few days and you can claim the digital badge and download the certificate; CySA+ is valid for three years under the CompTIA Continuing Education programme, renewed with 60 CEUs plus the $150 CE fee, or automatically by passing a higher-level CompTIA certification — diary the expiry immediately. On a fail, resist booking the immediate retake that the no-waiting-period policy makes possible; take the domain breakdown, identify the one or two areas that dragged the 750 down — often the Reporting/Communication domain for V4 candidates, or the new AI-in-security content — and spend a fortnight on those specifically. If you discover you were somehow booked for CS0-003 rather than CS0-004, that is a version error to correct before any retake, since CS0-004 is the current exam and CS0-003 English retires 22 December 2026. The score report tells you precisely where to aim, which is a luxury, and wasting it by re-sitting on the same knowledge is how a ~$439 voucher becomes a ~$878 one.
Reference
What are the key facts about the CompTIA Cybersecurity Analyst (CySA+)?
CompTIA Cybersecurity Analyst (CySA+) is a certification credential; awarded by CompTIA; the exam fee is $404; typical preparation is 3–4 months; holders typically earn $75,000 – $115,000.
| Credential | CompTIA Cybersecurity Analyst (CySA+) |
|---|---|
| Abbreviation | CySA+ |
| Type | Certification |
| Profession | IT, Cloud & Cybersecurity |
| Specialty | CompTIA |
| Awarded by | CompTIA |
| Difficulty | Hard |
| Typical prep time | 3–4 months |
| All-in cost | $404+ |
| Typical salary range | $75,000 – $115,000 |
| Exam code | CS0-003 |
| Scope | National / Multi-state |
| Also known as | CS0-003 |
Real questions
Frequently asked questions about the CompTIA Cybersecurity Analyst (CySA+)
Is CySA+ harder than Security+?
Yes. It assumes Security+ and adds behavioral analytics, threat hunting and hands-on response scenarios.
Where does it sit before CISSP?
CySA+ is a strong intermediate defensive cert; CISSP is a broader management-level cert that needs five years of experience.
How do I register for comptia-cysa-plus?
You register and schedule comptia-cysa-plus through Pearson VUE. Pick a test-centre appointment or online proctoring, then sit the exam on your booked date.
What is the comptia-cysa-plus exam format?
The exam is delivered as Multiple-choice and performance-based, with about 85 items, in 165 minutes. The published pass mark is 750 of 900.
How long is the comptia-cysa-plus certification valid?
Most CompTIA certifications are valid for three years and renewed via Continuing Education (CE) credits, a higher cert, or a single renew-by-exam.
How much does comptia-cysa-plus cost?
The exam fee is $404. Optional study materials and retakes are priced separately.
Who issues the Linux+ certification?
CompTIA (the Computing Technology Industry Association), a vendor-neutral certifying body. The exam is delivered through Pearson VUE and the credential is ANSI-accredited to ISO/IEC 17024.
How do I renew a CompTIA certification?
Through CompTIA CertCentral: accumulate the required Continuing Education (CE) credits (50 for Linux+) and pay the CE fee, earn a higher CompTIA cert, or retake the current exam. Most CompTIA certs follow the 3-year renewal cycle.
Are CompTIA exam vouchers refundable?
Vouchers are typically non-refundable but may be transferable and carry an expiry date. Optional training products may have a limited refund window. Always review the terms shown at purchase in the CompTIA store.
In short
Is the CompTIA Cybersecurity Analyst (CySA+) worth it?
- CySA+ focuses on defensive analytics and response.
- It builds on Security+ with hands-on scenarios.
- It renews every three years.
Same awarding body
What other credentials does CompTIA award?
Worth comparing
How does the CompTIA Cybersecurity Analyst (CySA+) compare with similar credentials?
Trust
Where does this information come from?
Everything above is taken from the awarding body's own published material. Fees, question counts and domain weights are revised regularly — check the official page before you pay.
- CompTIA Awarding body
- Official CompTIA Cybersecurity Analyst (CySA+) exam page Exam page
- CompTIA certification programme Programme rules
Research confidence: high · Last reviewed 2026-08